ReadyOn Implements Four Walls Multi-Tenant Architecture on Amazon EKS to Secure Enterprise Workforce Intelligence Platforms

In the modern landscape of enterprise information technology, securing multi-tenant environments remains one of the most persistent and critical engineering challenges. ReadyOn, an Amazon Web Services (AWS) Partner specializing in intelligent labor orchestration platforms for Fortune 100 enterprises, has unveiled a comprehensive defense-in-depth architecture designed to eliminate cross-tenant data exposure risks. Operating a multi-tenant platform on Amazon Elastic Kubernetes Service (Amazon EKS), ReadyOn processes highly sensitive enterprise data—including payroll records, complex organizational hierarchies, and operational analytics spanning hundreds of thousands of employees. Because a security breach or accidental cross-tenant data access could trigger severe regulatory compliance obligations across multiple jurisdictions and critically damage enterprise trust, the company engineered an advanced security paradigm known as the "Four Walls" model.
The Vulnerability of Default Kubernetes and the Multi-Tenancy Threat Model
Kubernetes has rapidly become the operational backbone for scalable, cloud-native applications, yet out-of-the-box deployments present significant security surfaces. Historically, upstream Kubernetes configurations have permitted anonymous requests to reach the API server, where access was restricted solely by Role-Based Access Control (RBAC). Furthermore, default container deployments often execute pods with root privileges, and native network policies do not exist until administrators explicitly define them.
While hardening single-tenant clusters is a well-documented engineering objective, introducing multi-tenancy fundamentally alters the threat model. In a shared environment, the central security concern shifts away from whether an unauthorized external actor can breach the perimeter to whether Tenant A can inadvertently or maliciously access the private data of Tenant B. Historically, many multi-tenant Kubernetes platforms have relied heavily on a single isolation mechanism: the namespace. However, Kubernetes architects never intended namespaces to function as unbreachable security boundaries. Recognizing that a single wall is insufficient for protecting enterprise payroll and workforce data, ReadyOn developed an architecture that enforces four independent, overlapping layers of isolation across the entire technology stack.
Anatomy of the Four Walls Architecture
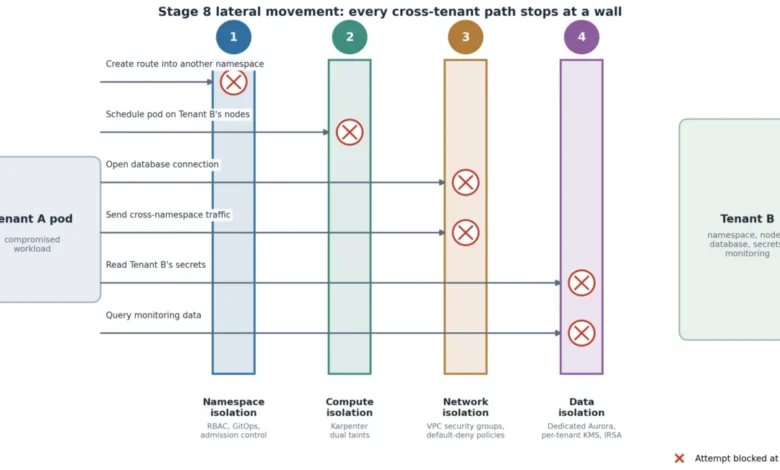
The core philosophy behind ReadyOn’s Four Walls model is compound defense. To successfully breach a tenant boundary, an unauthorized actor or compromised process must simultaneously bypass four entirely independent barriers, each operating at a fundamentally different layer of the infrastructure stack and requiring distinct techniques to compromise.
The first barrier operates at the Kubernetes API layer through rigorous namespace isolation, GitOps-enforced consistency, and strict admission controllers. Every tenant namespace is automatically provisioned using Argo CD ApplicationSets driven by declarative configuration files maintained within a Git repository. When a new enterprise client is onboarded, a single configuration entry triggers automated generation of all required resources, including namespaces, network policies, RBAC bindings, resource quotas, and secret configurations. This GitOps-driven approach eliminates the existence of legacy tenants with weaker security postures, ensuring that every customer receives an identical, hardened configuration by design.
Furthermore, strict RBAC bindings restrict API access exclusively to a tenant’s designated resources, while admission controllers evaluate all incoming manifests to block privileged configurations, container root executions, and unauthorized resource types such as DaemonSets or ClusterRoles. A self-healing drift correction loop continuously compares the live cluster state against the declared state in Git, automatically reverting any manual modifications or unauthorized alterations within seconds without human intervention.
Compute Isolation and Karpenter Integration
Moving down the abstraction stack, the second wall shifts the isolation boundary to the compute layer—the physical or virtual machines where tenant code executes. In ReadyOn’s Harmony platform, workloads belonging to different tenants never share underlying compute nodes.
To achieve absolute compute separation, ReadyOn utilizes Karpenter, an open-source, high-performance Kubernetes cluster autoscaler built for AWS, configured with a dual-taint strategy. Karpenter provisioners generate worker nodes equipped with a unique tenant-identifier taint (such as tenant=acme-corp) and a specific workload-type taint (such as workload=frontend). Consequently, a pod must explicitly tolerate both taints to be scheduled. This ensures that Tenant A’s frontend nodes remain entirely isolated from Tenant A’s batch processing nodes, while both sets of infrastructure are physically and logically separated from Tenant B.
To prevent misconfigurations or malicious attempts to bypass this scheduler logic, admission controllers validate that a pod’s requested tolerations match its corresponding namespace identity. Additionally, all application nodes enforce Instance Metadata Service Version 2 (IMDSv2) with strict hop limits to thwart container metadata access exploits, while instance IAM roles are tightly scoped to single-tenant resource boundaries.
Network Segmentation at the Amazon VPC Layer
While the first two walls operate within the software abstractions of Kubernetes, the third wall drops below the container orchestrator entirely, enforcing rigorous isolation at the Amazon Virtual Private Cloud (Amazon VPC) and security group level.
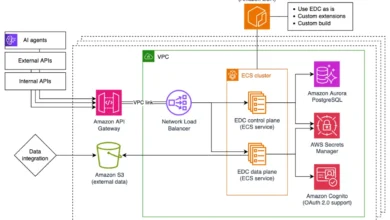
Within this architecture, each tenant’s dedicated Amazon Aurora database cluster is protected by an exclusive security group that accepts inbound connections solely from the security group attached to that specific tenant’s application nodes. As a result, Tenant A’s compute nodes are physically incapable of opening a TCP connection to Tenant B’s database. This isolation is enforced directly by the AWS software-defined network, meaning that bypassing it would require defeating the underlying cloud networking infrastructure.
The overarching VPC is meticulously structured into four distinct tiers: a public perimeter tier dedicated exclusively to load balancers; an application tier housing EKS worker nodes within private subnets; a database tier containing Aurora clusters devoid of internet access; and a control plane tier housing the private EKS API endpoint, accessible only via secure VPN connections integrated with OpenID Connect (OIDC) and Multi-Factor Authentication (MFA). Furthermore, default-deny Kubernetes network policies ensure that inter-namespace traffic is entirely prohibited unless explicitly authorized.
Data-Layer Isolation and Cryptographic Separation
The fourth and final wall addresses the ultimate asset: the data itself. Even in the highly improbable event that an attacker successfully compromises the preceding Kubernetes, compute, and network layers, Wall 4 ensures data security remains intact.
Rather than utilizing shared databases that rely entirely on application-layer query logic—where a single missing filtering clause could result in catastrophic data leakage—ReadyOn provisions dedicated Amazon Aurora clusters for every individual tenant. Because each tenant utilizes a completely separate database instance, there are no shared tables, and application code lacks the endpoint, credentials, and network routing required to reach another customer’s database.
To fortify data-at-rest security, each dedicated Aurora cluster is encrypted using a unique AWS Key Management Service (AWS KMS) customer-managed key specific to that tenant. Consequently, even if raw underlying storage volumes were somehow accessed, one tenant’s encryption key cannot decrypt the data of another. This level of cryptographic isolation is exceedingly difficult to achieve in shared database architectures where multiple tenants coexist within the same storage pools.
Workload Hardening and Operational Implications
Complementing the Four Walls structural model, ReadyOn enforces stringent container workload hardening across the Harmony platform. Every container executes in strict adherence to Kubernetes Pod Security Standards at the "restricted" level, enforcing non-root execution, disabling privilege escalation, mounting root filesystems as read-only, dropping all unnecessary Linux capabilities, and applying default seccomp profiles. This rigorous posture prevents container escape techniques from yielding useful system-level privileges or credentials.
Furthermore, the platform completely eliminates long-lived workload credentials. Workloads authenticate to AWS APIs exclusively through short-lived JSON Web Tokens issued by the AWS Security Token Service via OIDC federation, leveraging IAM roles strictly scoped to individual tenant resources. Credentials expire automatically within minutes, neutralizing the risk of static credential theft.
Industry Implications for Cloud-Native Security
As enterprises increasingly migrate sensitive workloads, financial systems, and workforce data to managed Kubernetes environments like Amazon EKS, the ReadyOn Four Walls model offers a compelling architectural blueprint for zero-trust multi-tenancy. By systematically combining native Kubernetes controls, advanced node provisioning with Karpenter, AWS software-defined networking, and dedicated database encryption tiers, organizations can achieve uncompromising security without sacrificing the operational agility, scalability, and economic efficiency inherent in cloud-native multi-tenant platforms. Regular adversarial testing and automated drift correction further validate that defense-in-depth remains the most reliable strategy for protecting critical enterprise assets in modern distributed computing environments.